NCM operations
The NCM GitHub App checks the dependencies in your pull requests and deployments against NodeSource Certified Modules (NCM) rules, and reports the results in NodeSource Accounts under NCM Operations. This page explains how to install and configure the app and where to find its reports.
Overview
The NCM integration with GitHub (gates and deployment protection rules) helps you keep your dependencies secure and high quality. It catches issues early in development, which reduces the risk of shipping security vulnerabilities.
NCM GitHub App integration
Add the NCM - NodeSource GitHub App (gates and deployment protection rules) to your repositories from the GitHub Marketplace. After you add it, the app analyzes each pull request and deployment and sends a report to NodeSource Accounts. The NCM app only works for public repositories that belong to an organization.
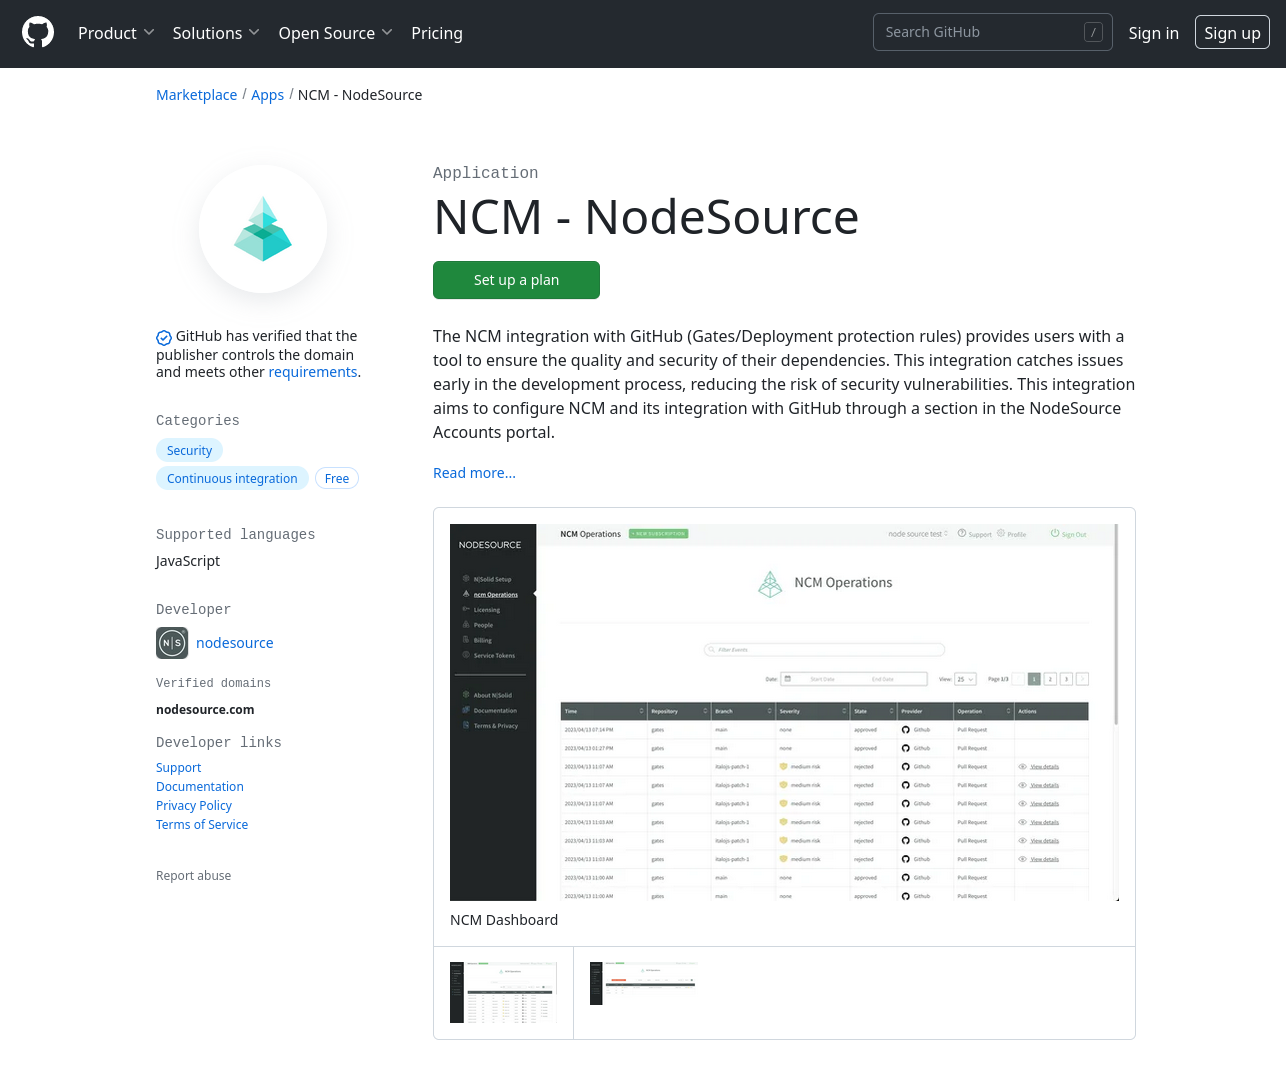
NCM GitHub configuration
To use the NCM app, install it on a GitHub organization that has at least one public repository. Then, in the repository settings, select NCM in the deployment protection rules.
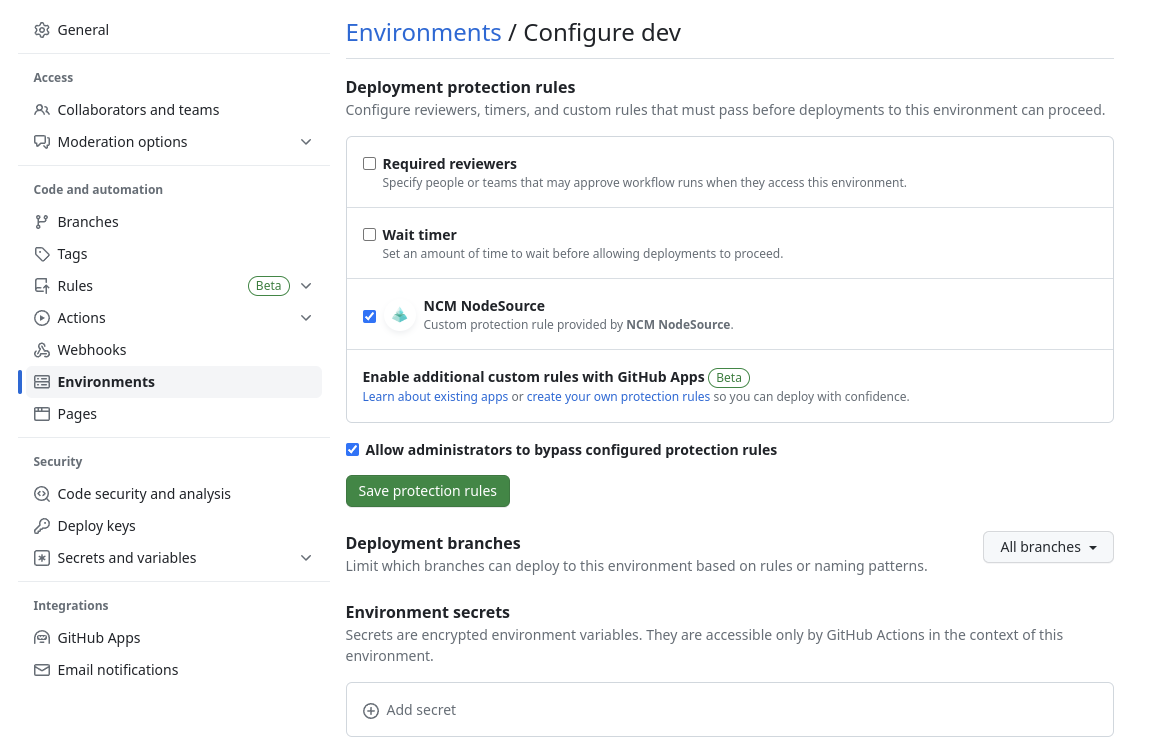
Once the deployment rule is in place, you can start using the NCM app.
NCM Operations in NodeSource Accounts
Select NCM Operations in the left navigation of NodeSource Accounts to see NCM's results for each pull request or deployment in your repositories. The page shows a summary of each analysis and a link to a detailed report.
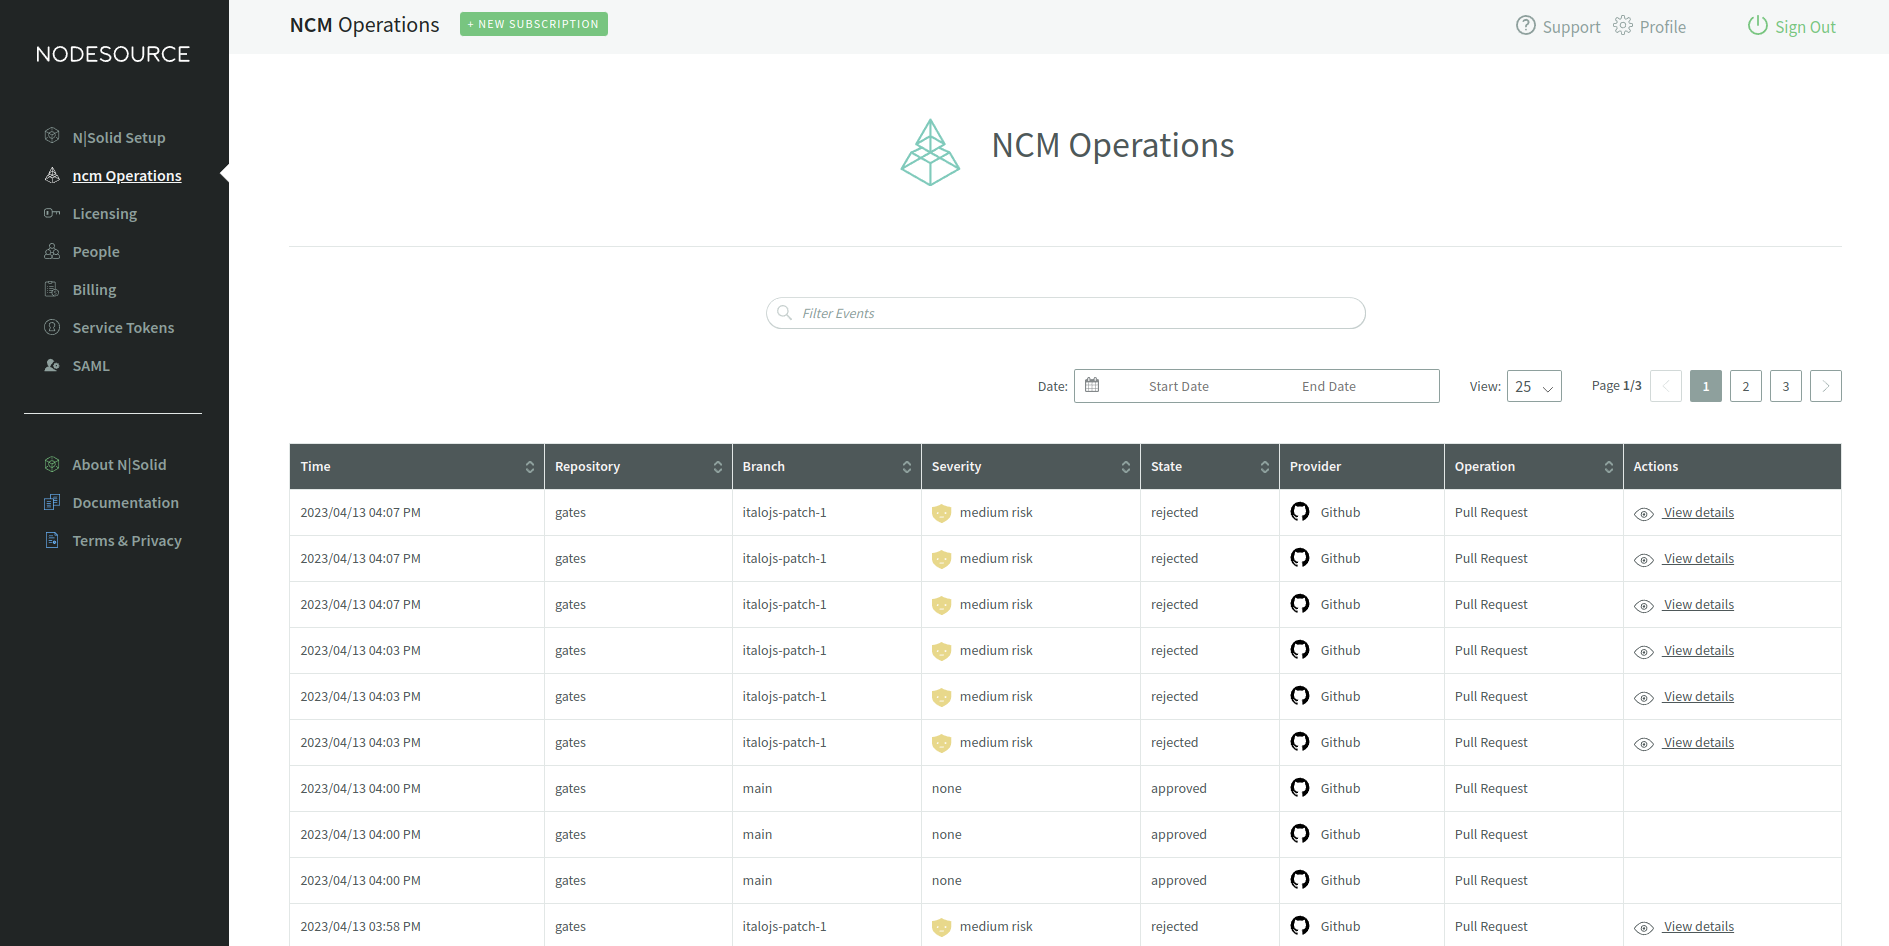
To see the detailed report, click View Details.
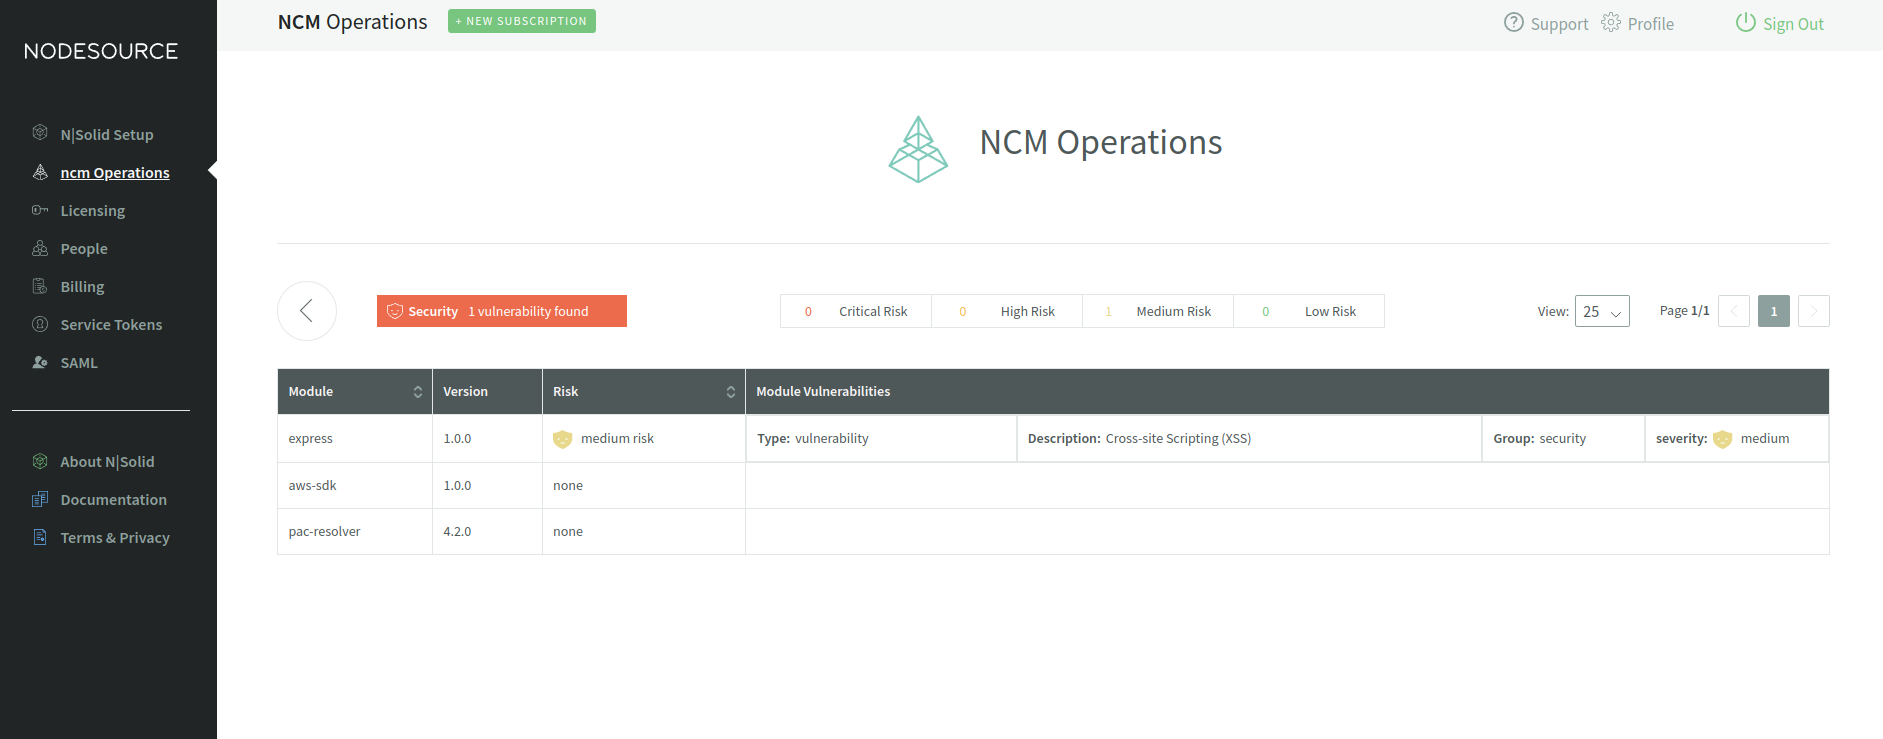
Deployment approval
NCM validates every deployment flow configured in GitHub and approves or rejects it according to your NCM rules. If NCM rejects a deployment, it provides a detailed report that explains why. NCM is triggered by webhook events from GitHub.
NCM pull request checks
NCM checks each pull request in a repository where the NCM GitHub App is installed. It attaches a report and marks the pull request status green or red based on the issues found, with recommendations for fixing them.
Security
The NCM GitHub App is registered with GitHub using OAuth2 authentication, so only authorized users can access the app. The app also uses a private key to sign all requests, ensuring that only GitHub can send requests to the app.
The NCM app has read-only access to the repositories it is installed on, and read-only access to their pull requests and deployments. It can't access sensitive data or make changes.
