Role-based access control
Role-based access control (RBAC) lets organization admins decide what each member can see and do in NodeSource Accounts (accounts.nodesource.com) and the N|Solid Console. RBAC is available to Enterprise and Advanced tier users. This page describes the default roles, how to create and assign roles, and every available permission.
Permissions are grouped into roles. You can change the permissions of any role and create your own roles to match your team's workflow and access-control needs.
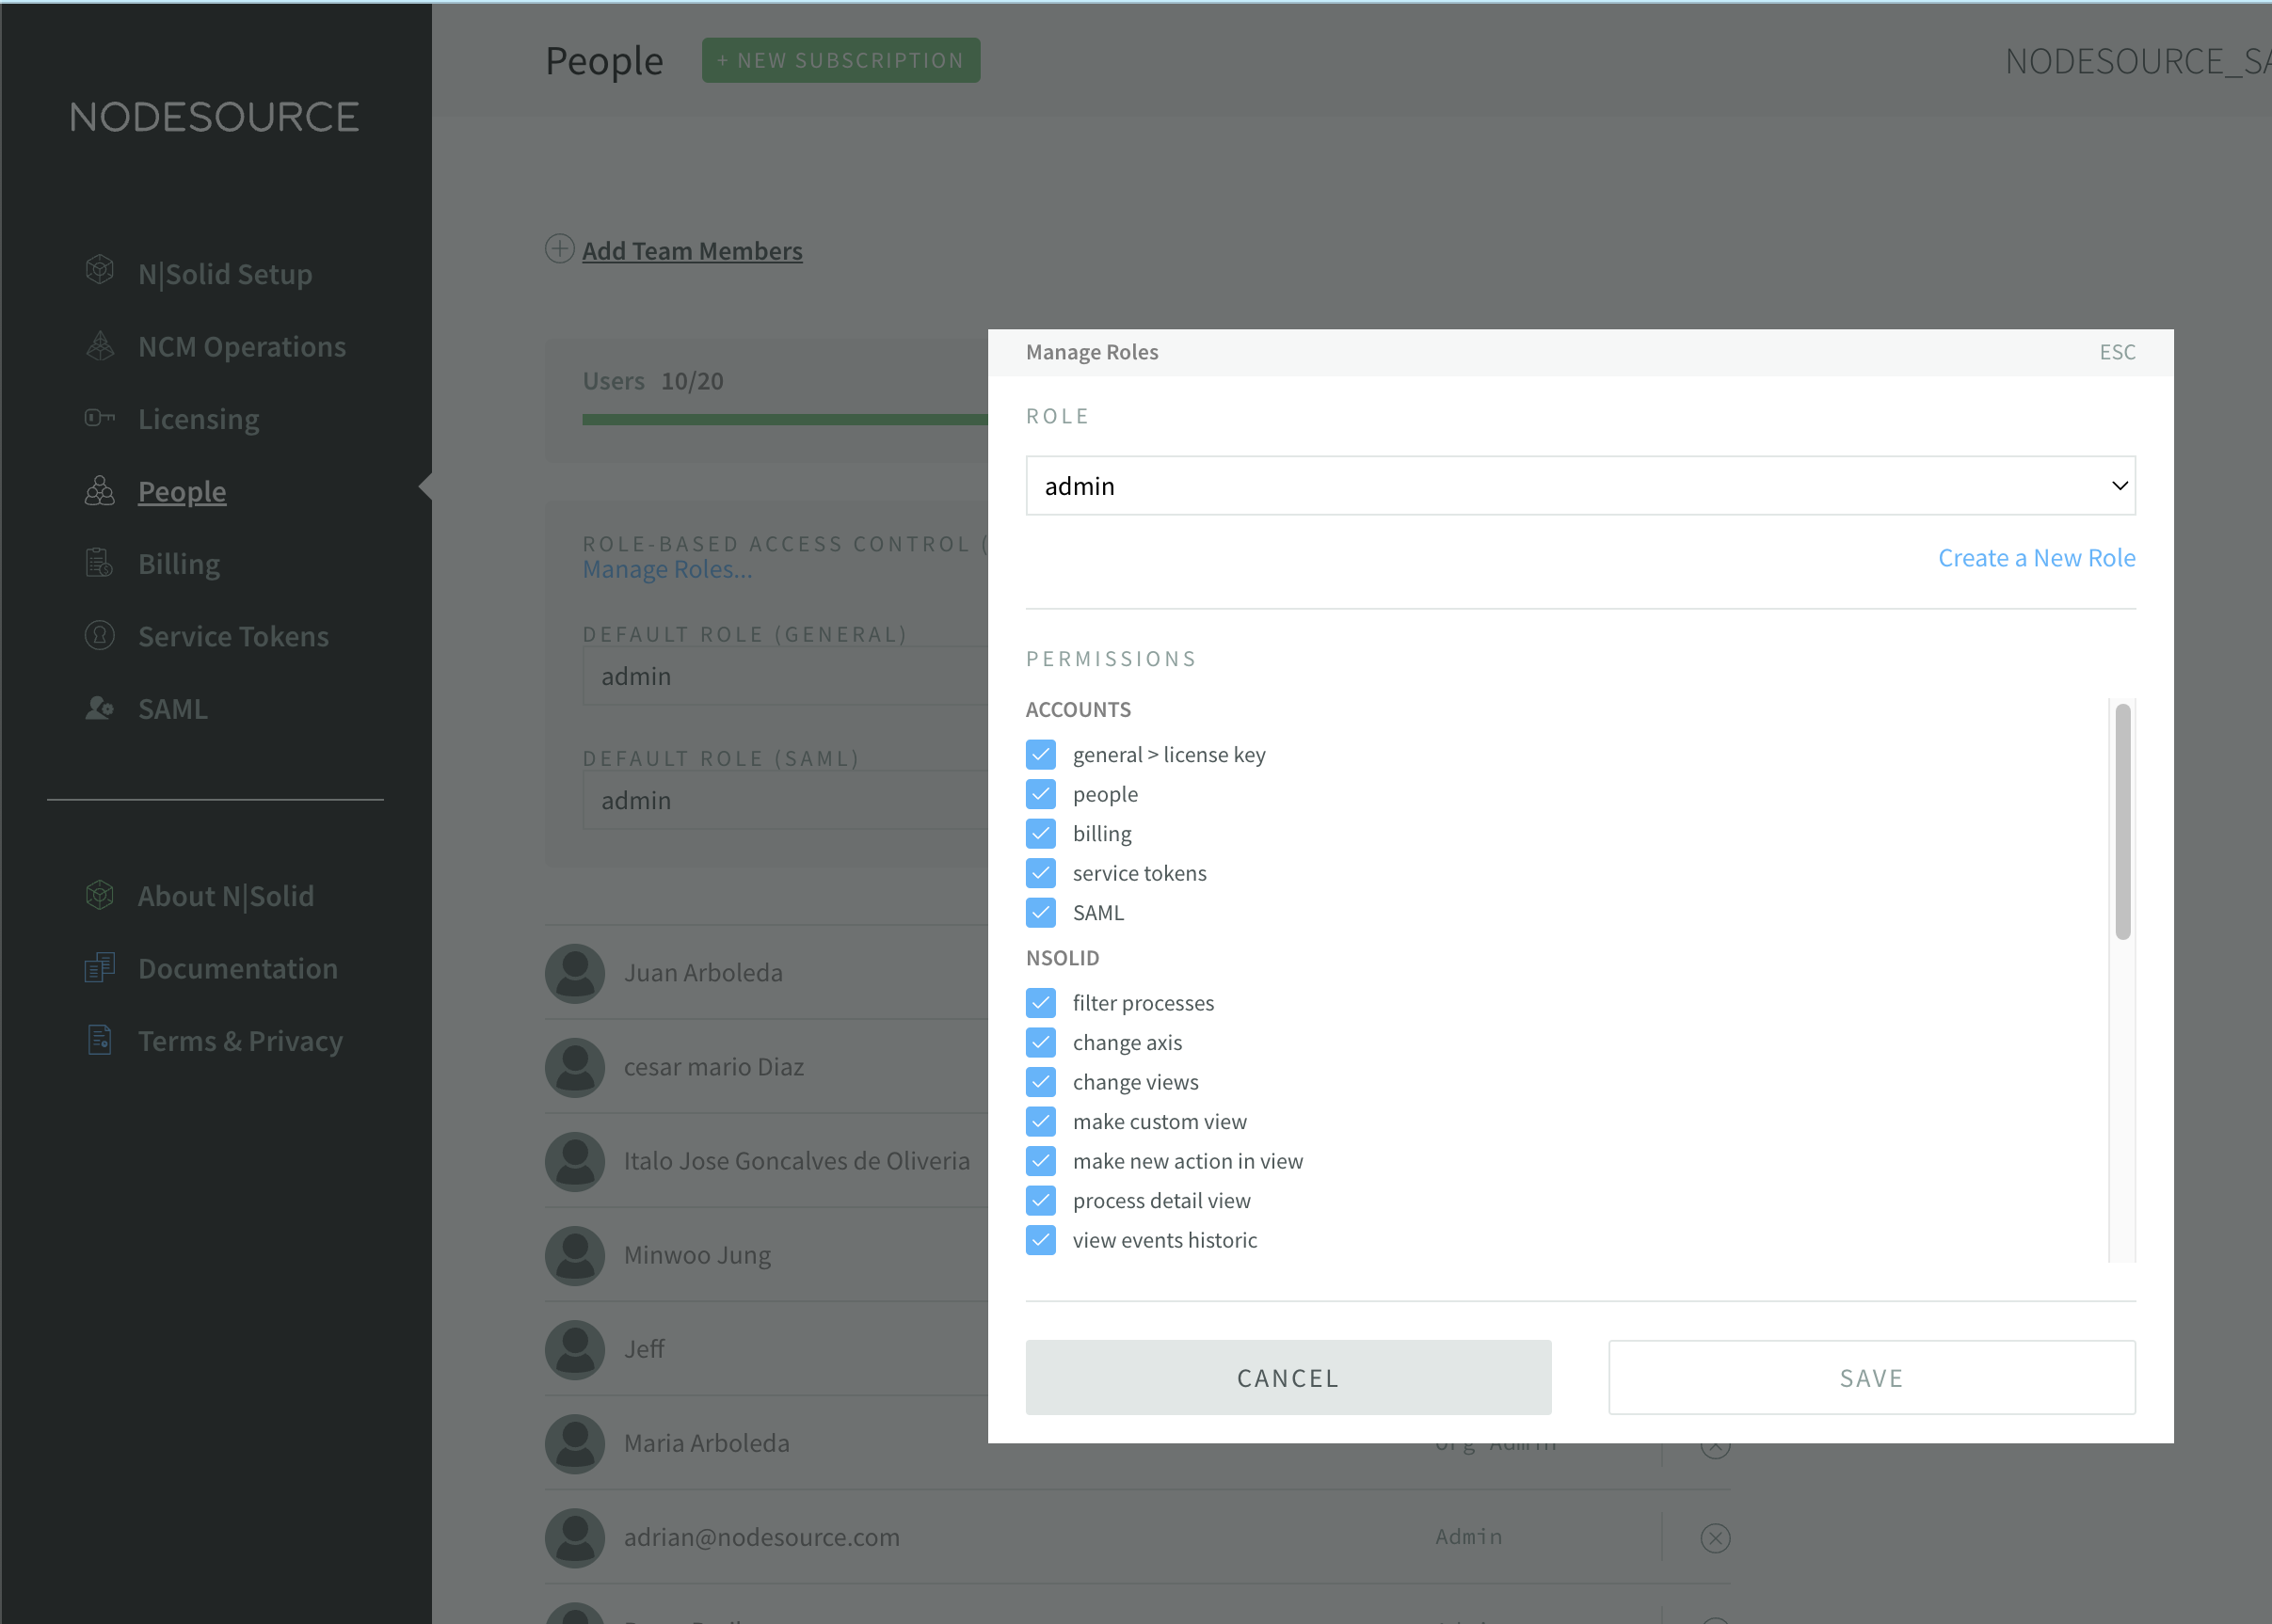
How it works
Admins create roles, choose the permissions each role includes, and assign roles to members. Each permission unlocks a specific action or view in NodeSource Accounts or the N|Solid Console.
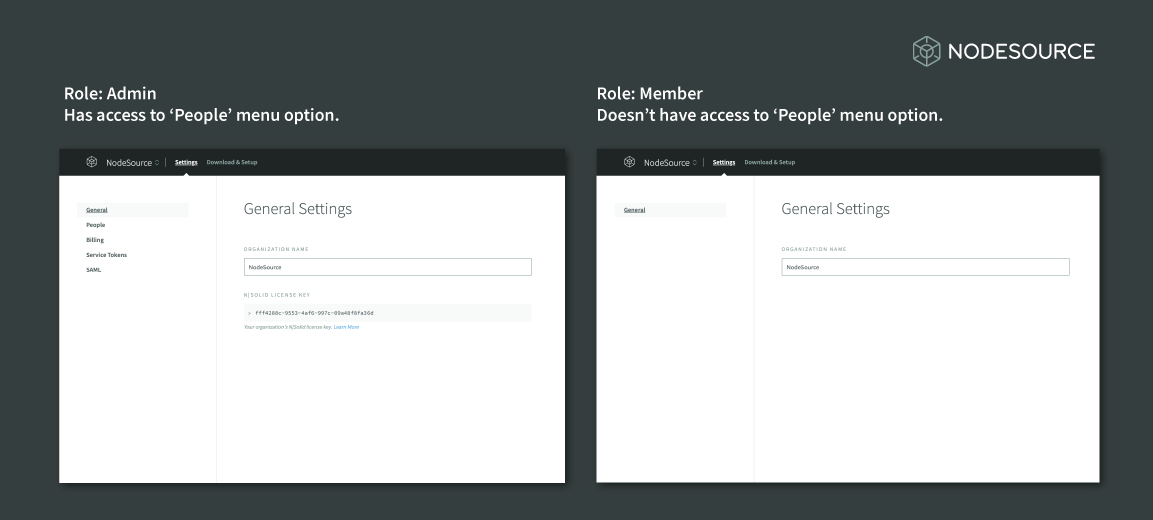
For example, in NodeSource Accounts:
- A member with the
adminrole can open People, invite team members, and define and assign roles. - A member with the
memberrole doesn't have the people permission, so People isn't shown.
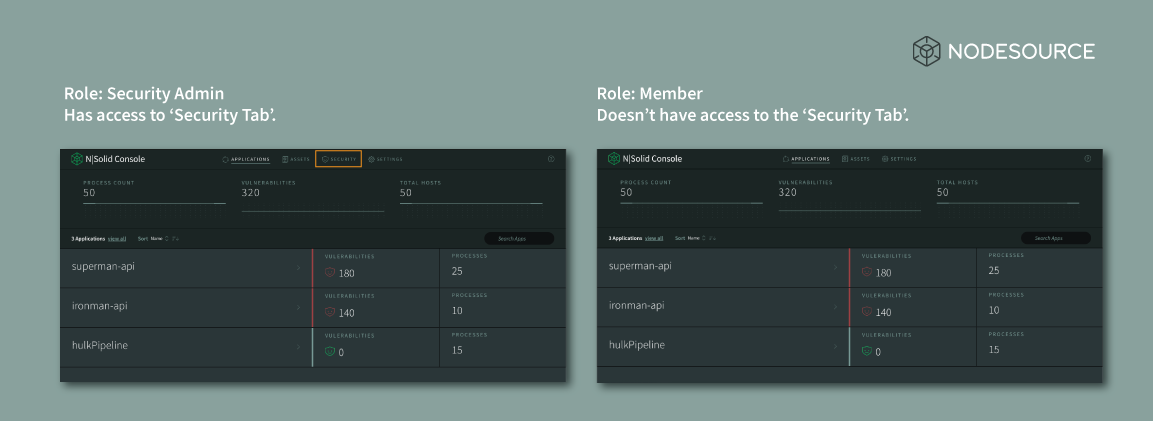
Similarly, in the N|Solid Console, a member whose role includes view security vulnerabilities can open the Security view, and a member whose role doesn't include it can't:
Default roles
Every organization starts with four default roles:
| Role | Permissions |
|---|---|
admin | All NodeSource Accounts and N|Solid Console permissions, including all Console settings. |
opsAdmin | Everything in member, plus the diagnostics permissions dynamic configuration, generate cpu profile, generate heap snapshot, generate heap sample, generate sbom, and machine learning. Can't hide security vulnerabilities. |
securityAdmin | Console monitoring permissions, view security vulnerabilities, hide security vulnerabilities, assets, custom filters, and ai service complete agent. |
member | The same as securityAdmin, without hide security vulnerabilities. |
"Console monitoring permissions" means filter processes, change axis, change views, make custom view, make new action in view, process detail view, view events historic, show applications, and show functions.
Default roles can't be deleted, but you can change their permissions. Only admin includes NodeSource Accounts permissions such as people and billing.
Set default roles for new members
-
Sign in to accounts.nodesource.com and select your organization in the organization selector at the top left.
-
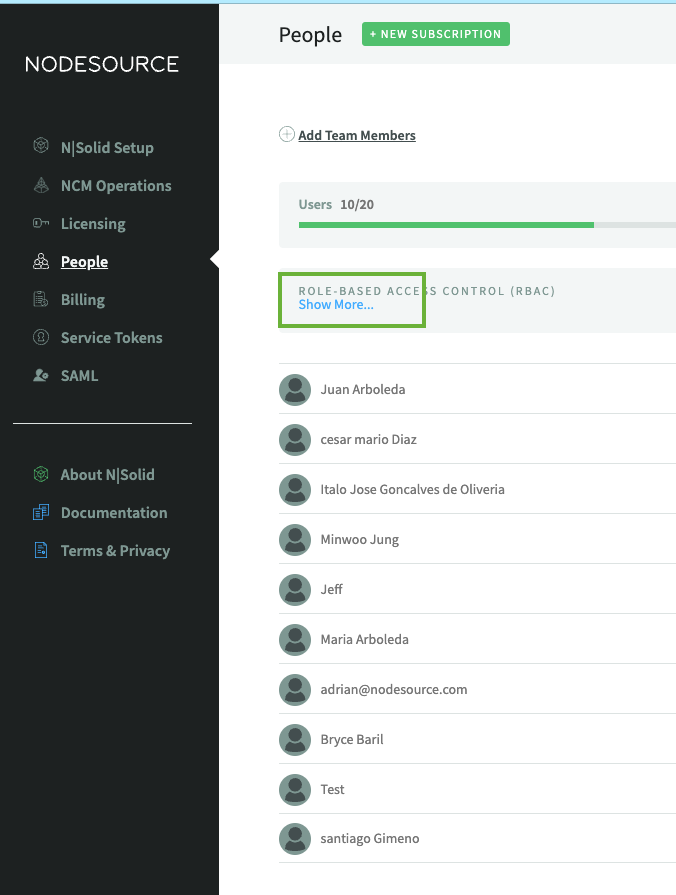
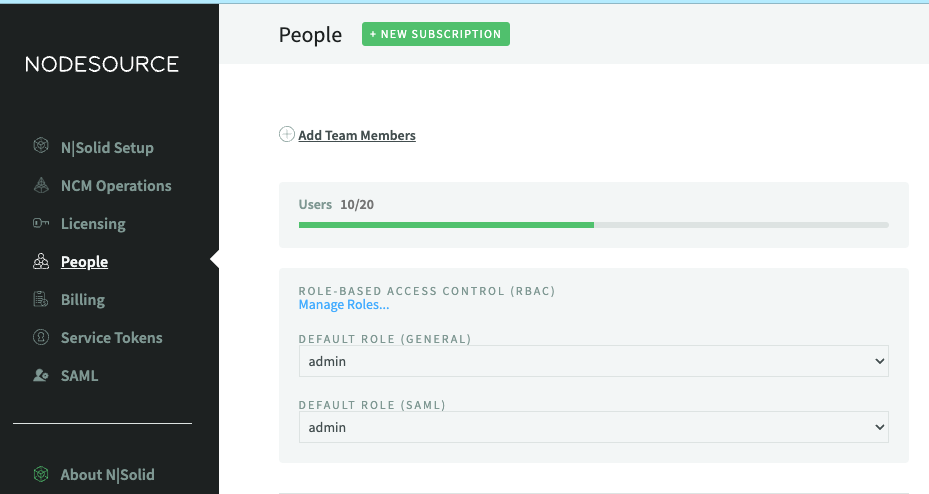
Select People in the left navigation, and click Show More... under Role-based access control (RBAC).
-
Choose the default role for new members. You can set one default for invited users (Default role (GENERAL)) and another for members who join through your organization's SAML configuration (Default role (SAML)).
Modify roles
-
Open People and expand the RBAC section as described above.
-
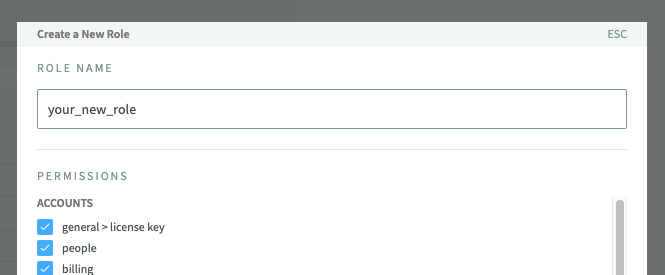
Click Manage Roles... to open the Manage Roles dialog.
-
In the dialog, change the permissions of an existing role, or create a new one. Each role is a set of permissions.
Anyone whose role includes the people permission can change the permissions of every role. Reserve this permission for your organization's admins.
Create a role
-
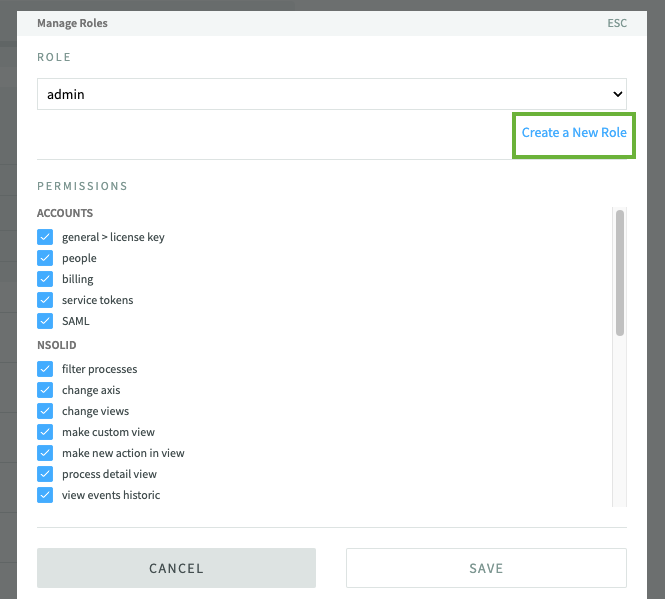
In the Manage Roles dialog, click Create a New Role.
-
Name the role and select the permissions it should include. The permissions are described in Available permissions.
Delete a role
To delete a custom role, click the delete icon next to it in the Manage Roles dialog. You can delete a custom role only if no members are assigned to it and it isn't set as Default role (GENERAL). Before you delete a role that is set as Default role (SAML), choose a different SAML default. Default roles can't be deleted.
Assign roles
After you save a role, you can assign it to members on the People page.
Available permissions
The Manage Roles dialog groups permissions under ACCOUNTS and NSOLID, and shows each permission by its ID with dashes replaced by spaces.
ACCOUNTS
| Permission | What it allows |
|---|---|
| general > license key | View the organization's N|Solid license key on Licensing. |
| people | Invite and remove members, assign and change roles, set default roles, and create and modify roles. |
| billing | Open Billing. |
| service tokens | Create, rename, regenerate, and delete service tokens. |
| SAML | Configure SAML single sign-on with Okta, PingOne, or OneLogin. Shown only for enterprise organizations. |
NSOLID
| Permission | What it allows |
|---|---|
| filter processes | Set process and reporting filters. |
| change axis | Change chart axes. |
| change views | Change views in the Console. Also required to delete a saved view's actions. |
| make custom view | Create, change, and delete custom (saved) views. |
| make new action in view | Add actions that run when a saved view's threshold is met, such as taking a heap snapshot or CPU profile, or sending a Slack, Microsoft Teams, webhook, PagerDuty, or email notification. |
| process detail view | Open the process detail view. |
| view events historic | View historical events and metrics. |
| view security vulnerabilities | Open the Console's Security view. |
| hide security vulnerabilities | Hide vulnerabilities in the Security view. |
| assets | View and download diagnostic assets. |
| custom filters | Create, change, and delete custom filters. |
| show applications | Show applications in the Console. |
| show functions | Show serverless functions in the Console. |
| dynamic configuration | Change a process's configuration from the Console and manage Configuration Sets in Settings. |
| generate cpu profile | Take CPU profiles. |
| generate heap snapshot | Take heap snapshots. |
| generate heap sample | Take heap samples. |
| generate sbom | Generate a software bill of materials (SBOM). |
| machine learning | Use machine-learning features. |
| settings > general settings | Change general Console settings, including the Console URL, license key and organization association, and asset retention. |
| settings > global notifications | Manage global notifications for new vulnerabilities and global events, such as a blocked event loop or a process exit. |
| settings > saved views | Change and delete saved views. |
| settings > integrations | Configure Slack, Microsoft Teams, generic webhook, PagerDuty, and AWS SQS integrations. |
| settings > import export settings | Import or export saved views, integrations, and global notifications. |
| settings > machine learning | Change machine-learning settings. |
| settings > mcp integrations | Configure MCP integrations for N|Solid Copilot. |
| settings > sourcemap storage | Configure external sourcemap resolution. |
The default roles also include ai service complete agent, which lets members use N|Solid Copilot. It isn't shown in the Manage Roles dialog, so you can't add it to or remove it from a role there.
Service tokens have their own permission list, which includes a few permissions that roles don't use, such as Security vulnerabilities, Sourcemap Upload, and N|Solid Benchmark. See Service tokens.
